When a conversation moves channels, trust should not move automatically
A September 29 Microsoft report on abused remote-management tools illustrates a broader rule: ordinary collaboration does not automatically authorize new device access.
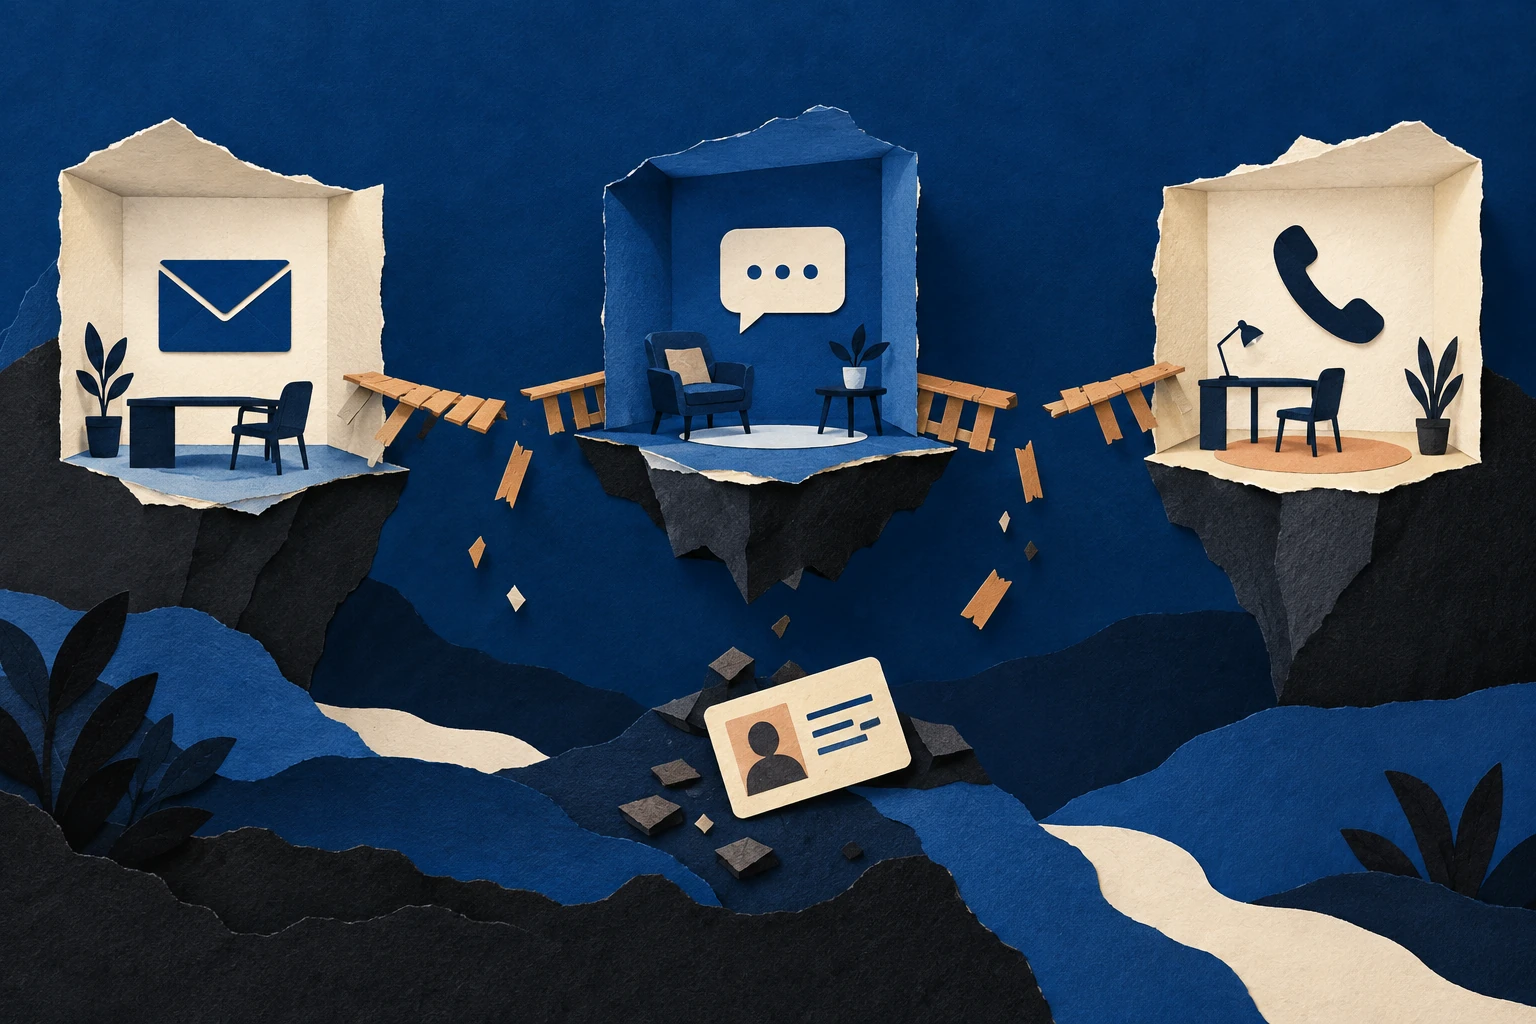
An email becomes a chat. The chat becomes a meeting. The meeting requires an update. The update installs a tool with access to the computer. To the person following along, this can feel like one continuous task. In security terms, several different decisions have occurred.
Continuity of conversation is not continuity of authorization. A person who may send you a document does not automatically have permission to choose software for your device. Someone invited to a call does not gain the right to control your screen. Each change in channel or capability creates a new boundary.
A fresh Microsoft report makes this distinction unusually concrete. It describes phishing that used familiar work activities to deliver legitimate remote-management software. The lesson is not that all collaboration tools are dangerous. It is that the story around a tool cannot establish who is authorized to use its power.
What Microsoft reported on September 29
In a September 29, 2026 analysis, Microsoft described activity observed in July 2026. Phishing lures associated with meetings, documents and software updates distributed disguised installers for legitimate MSP360 remote-management software. The researchers also observed installation of ScreenConnect, providing another remote-access channel.
Microsoft explicitly said it did not observe exploitation of ScreenConnect itself in this activity. The reported issue was unauthorized use of legitimate administration software, not evidence that the product was inherently malicious or that its vendor had been breached.
That is the source-based finding. Our broader inference is that the decisive moment was not only the first suspicious message: it was the point where an ordinary communication task became a request for durable device access.
Map the powers, not just the apps
A person can communicate with you.
A person can share a meeting or document.
A person or tool can act on your device or account.
App names can hide these differences. One collaboration product may support text chat, file sharing, screen viewing and remote control. Another may be used legitimately by IT administrators while having no legitimate role in a routine customer call.
Ask what changes after the requested action. Will another party see information? Can they move the pointer? Does software remain installed after the meeting? Is an account granting permissions to a separate application?
The answer determines the verification needed. It is more useful than asking whether the product has a familiar logo or whether a download carries a recognizable publisher name.
The psychological shortcut at the handoff
A conversation builds small commitments. You reply to a plausible message, arrange a time and join a call. By the time someone requests an additional step, refusing can feel like undoing work you have already agreed to do.
There is also a coordination problem. The other person appears to be waiting. A technical obstacle becomes your responsibility to solve. A request framed as “just the meeting update” can receive less scrutiny than the same request presented cold.
These are ordinary pressures, not evidence of weak intelligence. A good defensive workflow recognizes them and gives people a socially acceptable way to pause at a capability change.
Our guide to manufactured urgency examines the time-pressure element. Here, the key additional factor is momentum: trust earned for a small interaction gets carried into a more consequential one.
A boundary table for common handoffs
| Transition | New question | A practical independent check |
|---|---|---|
| Email to chat | Is this the expected person in the new channel? | Confirm through an established contact record |
| Chat to meeting | Is the invitation part of the agreed task? | Open the known meeting service independently |
| Meeting to installation | Why does this task require new software? | Check the organization’s approved software route |
| Screen viewing to control | Who needs to act, and with what limits? | Confirm an authorized support assignment |
| One-time help to persistent access | Why should access remain afterward? | Require explicit administrative approval and ownership |
This is an editorial decision aid, not a universal rule that every transition is suspicious. Many are normal. The point is to keep the additional permission visible instead of treating it as a minor extension of the earlier conversation.
A verified colleague can also make a mistaken request. Independent checking protects the task without requiring an accusation about the person.
Why a legitimate download does not settle the question
Software authenticity answers an important question: where the software came from and whether it has been altered in ways that its verification mechanism detects. It does not answer whether this person should install it for this purpose.
A remote-management tool can be correctly signed and still be configured for an unauthorized operator. A real file-sharing service can host an unwanted file. A valid meeting platform can carry a fraudulent invitation.
The FBI’s phishing guidance similarly emphasizes verifying communications and avoiding untrusted routes into accounts or actions. Familiar branding is not sufficient evidence of a requester’s authority.
Keep the authenticity question and the authorization question separate. “This is genuine software” may be true while “this installation is approved” is false.
Give people an alternative that preserves the task
A boundary is easier to maintain when the user can offer another way forward. For a meeting, that may be an approved browser option or an invitation through the organization’s normal system. For a document, it may be a supported file format sent through an established channel.
The alternative should not require the recipient to diagnose malware. It should simply keep the work within known tools and permissions. A genuine business contact can then coordinate with the organization’s support process if an exception is necessary.
Do not frame this as a contest in which every refusal proves malicious intent. Some legitimate organizations have awkward workflows. The safe conclusion is that the requested action is not yet authorized, not that the person has been conclusively identified as an attacker.
That distinction keeps verification firm without turning routine collaboration into confrontation.
The support exception needs its own identity
Remote support is a legitimate reason to grant additional access. It should therefore have a stronger identity path than “someone in the meeting says they are IT.”
An approved support ticket, a technician assignment visible through the organization’s established system and a clear explanation of the permissions can connect the person to the task. The support session should also have a defined end and an accountable owner.
Our analysis of email bombing followed by a Teams support approach shows why this matters during disruption. A real problem can make the first available helper seem authenticated by their usefulness.
If email is unavailable, the fallback support route should already exist. Inventing a new route during an incident gives the person creating the pressure too much control over the response.
If the boundary has already been crossed
Tell the responsible support or security team exactly which capability was granted. “I clicked a link” is useful but incomplete if it led to software installation, administrative approval or remote control.
Record the original contact, the sequence of channels, the software name, the approximate time and any permission prompts you remember. Preserve available messages and follow the organization’s containment instructions.
Closing a call or deleting the initial email does not necessarily end software-based access. Conversely, receiving a suspicious invitation without acting on it does not establish that the device was compromised.
Recovery needs evidence about the actual actions. Avoid running cleanup tools recommended by the same unverified contact, and do not enter fresh credentials while a suspicious remote session remains active.
What managers can change without a new security product
Make approved meeting, document and support routes easy to find. State which installations employees may perform themselves and where exceptions go. Provide a clear way to decline unapproved software without losing access to essential work.
Review how external collaborators are onboarded. If every supplier uses a different ad hoc process, employees repeatedly face ambiguous decisions. A small set of supported alternatives can reduce that burden.
Give managers an explicit role: they should support a pause when a task suddenly requires more access. If delivery pressure consistently overrides verification, the written policy will not describe the real organization.
Finally, review remote-management inventory with the responsible technical team. The question is not just which products exist, but who owns each installation and whether its operator and purpose are authorized.
A simple exercise in permission awareness
Take a fictional workflow from an ordinary email to a completed meeting. Ask participants to mark every point where a new party gains a capability. Do not include real credentials, live suspicious links or operational attack steps.
Most groups will find decisions they previously treated as setup: installing an extension, allowing a browser permission, granting screen control or signing into a second service.
For each point, name the evidence that would justify it and the safe alternative if that evidence is missing. This produces a practical map of responsibility, not a test of who spots the most alarming words.
The desired habit is a small pause at a meaningful boundary. That is more sustainable than treating every message as an emergency—and more protective than assuming one legitimate beginning makes every later step legitimate.
Found a factual error or a source that has changed?
Send a correction →

