The dangerous part of a consent screen is what comes after “Allow”
A genuine identity provider can correctly process a permission request that you should never have approved. Read the app, scope and purpose as a separate access decision.
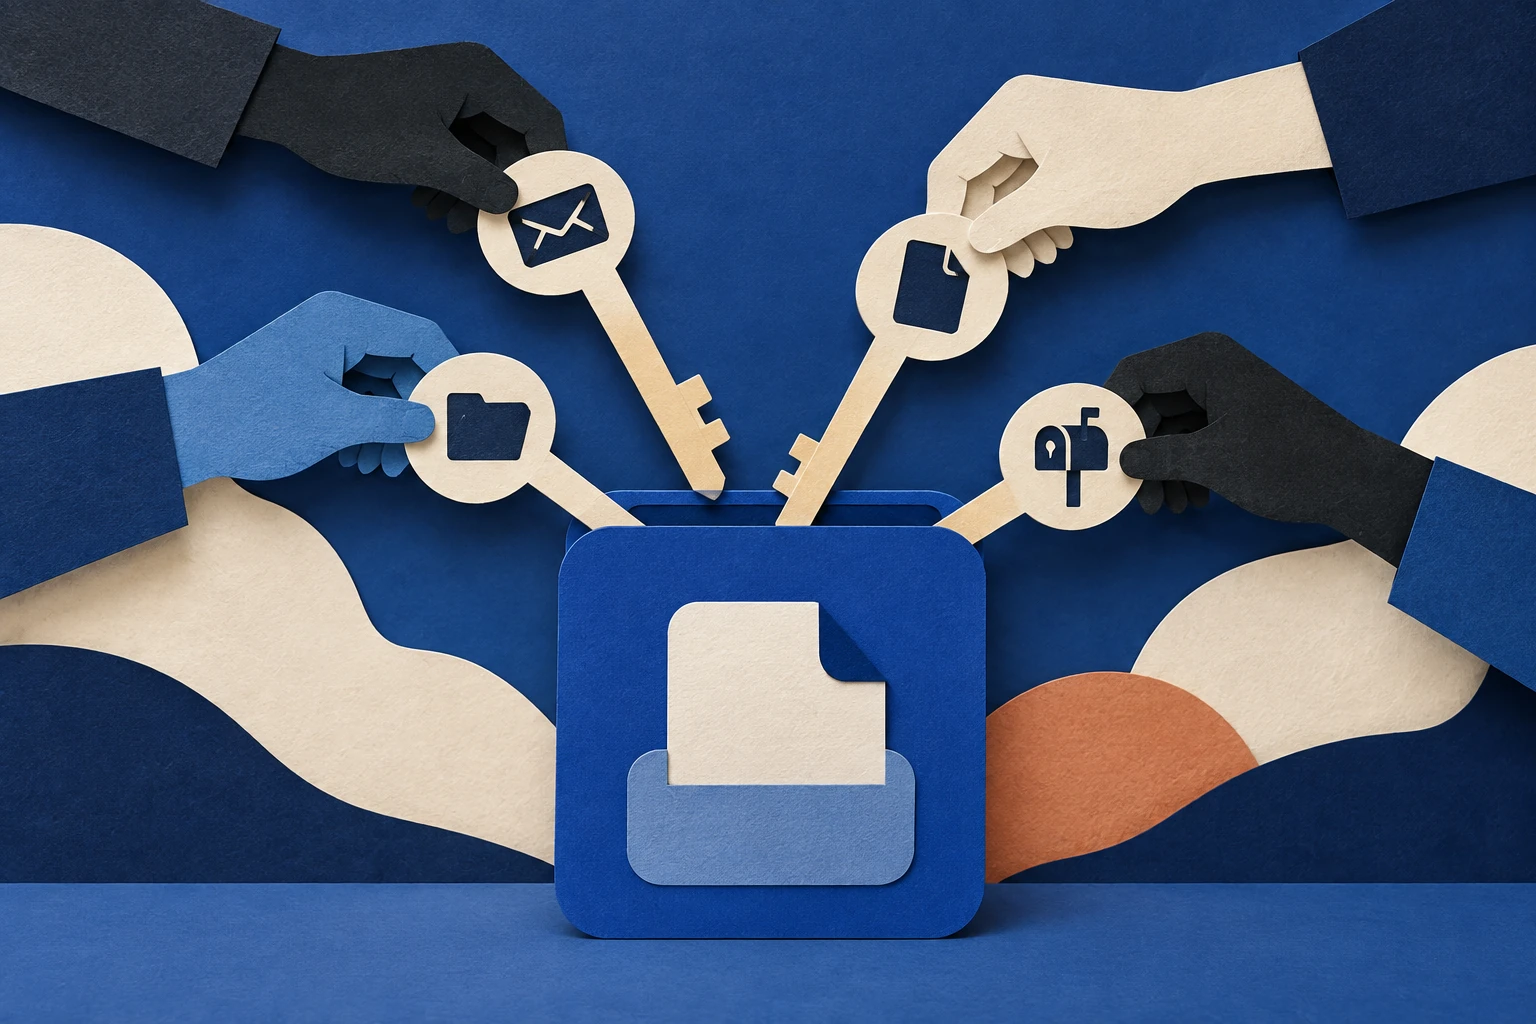
A familiar provider asks whether an application may access your account. You are already trying to open a document or connect a useful service, so the prompt feels like one more login step. The provider is real, the account is yours, and the button is clearly labeled. What could be wrong?
The answer lies in what the button authorizes. Authentication establishes who you are; consent can establish what another application may do with your data. Those decisions can appear next to each other without being the same decision.
A malicious request does not have to steal a password if it persuades you to grant access through the provider’s legitimate machinery. That makes the permission list—not just the sign-in address—the important part of the screen.
Read the screen as a contract of access
There are usually several objects to identify: the account you are using, the application requesting access, the publisher behind it, the permissions requested and the task that supposedly requires them. If any of those is unclear, the request is not ready for approval.
Which application and publisher receive access?
Which data or actions are included?
How does that scope fit the task you intended?
Do not treat a long permission list as background legal text. It describes capabilities. Reading mail, modifying files, sending messages and maintaining access are materially different from identifying your basic profile.
The exact meaning depends on the platform and permission. A reader should not infer technical details from a short label alone. Use the provider’s explanation or an administrator’s review when the scope is unclear, especially for a work account.
What consent phishing changes
Microsoft’s consent-phishing documentation defines the problem as users being tricked into granting permissions to malicious cloud applications. It explains that the legitimate identity platform can host the consent experience, which helps the request appear trustworthy.
That is distinct from a counterfeit login form. In a counterfeit form, the attacker may collect credentials. In consent phishing, the provider can issue access according to the permission the user approved. The malicious element is the application or purpose receiving that access.
Microsoft’s explanation of OAuth consent phishing provides further background on this authorization model. Neither source means that OAuth itself is inherently unsafe. Delegated access is useful; the problem is granting it to an untrusted or inappropriate recipient.
A task-to-permission comparison
Suppose an illustrative application says it needs to display one shared document. The screen asks for broad access to mail and files. The relevant question is not whether the app’s name resembles the document service. It is whether the requested capability makes sense for the task.
| Intended task | Question for the permission review |
|---|---|
| Sign in to identify yourself | Why is access to message content required? |
| View one shared file | Why does the app need broader file access? |
| Add a calendar feature | Can access be limited to the necessary calendar operations? |
| Connect a work service | Is this an approved application with an accountable owner? |
| Complete a one-time action | Does the request establish continuing access? |
These are questions, not universal verdicts. Some legitimate applications need substantial permissions. The burden is to understand and justify the scope, not to assume that any broad permission is malicious or that any narrow permission is harmless.
A mismatch should trigger review. It should not trigger a guessing game in which the user invents a technical reason for whatever the application asks.
The publisher signal has limits
A recognizable or verified publisher can help establish provenance. It does not tell you that every requested permission is appropriate for your organization or your task. A legitimate vendor can offer a feature that is unnecessary for the data you hold.
Similarly, an application name is not a security boundary. Names and icons can resemble familiar services. Do not approve solely because the text looks like an internal tool or a widely used product.
For a work account, use the organization’s approved application catalog or support process where available. If the app is not listed, ask who owns the integration and what review it has received. A colleague’s recommendation is useful context, but it is not necessarily authorization to expose organizational data.
Our device-code explainer describes another case in which a real login page does not settle the destination of access. Keep the mechanisms separate while retaining the broader question: who benefits from the action you are approving?
The approval request can be hidden inside a different story
A message may begin with a document, meeting, invoice or security notice. By the time the consent screen appears, the reader has mentally committed to completing that earlier task. The access request is interpreted as a technical requirement rather than a new choice.
This is a common design problem even outside malicious activity. Interfaces often reward completion and make refusal feel like failure. In a security context, the user needs explicit permission to stop when the request changes.
A useful instruction is: “If the task becomes an access grant you did not expect, pause and verify the application.” That is more actionable than “Only click Allow when safe,” which simply repeats the decision the person is struggling to make.
Do not let the sender’s urgency define the review. A genuine document can usually be provided through another approved route while the integration is checked.
If you approved something you now distrust
Report the application name, account, time and visible permissions through your provider’s or organization’s official support route. Preserve the message that led to the prompt. Do not revisit the suspicious flow to reproduce the consent screen if doing so could grant more access.
Review connected applications or account permissions through the genuine settings. Revoke unauthorized grants using the provider’s documented controls, and involve an administrator where organizational permissions or shared data are involved.
A password change may be appropriate if credentials were also exposed, but it should not be assumed to remove every application grant. Access granted to an app is a separate object that needs review. Our account-response model explains why recovery should inventory credentials, sessions, grants and devices rather than treating them as one thing.
Revocation also does not necessarily undo data already accessed or actions already taken. The responsible team may need to review logs, messages, files or downstream effects according to the scope of the permission.
For small organizations: establish an app owner
A common gap is that nobody owns the decision. An employee wants a useful tool, the tool asks for access, and the organization has no quick way to approve or decline. The employee becomes the de facto security reviewer.
Assign an accountable owner for integrations. Keep a short record of the app, business purpose, approved permissions, data involved and review date. The record does not need to be elaborate to be better than an unexplained collection of grants.
Make removal part of the lifecycle. If the project ends, the employee leaves or the tool is no longer used, review whether its access should remain. An application that was justified a year ago may no longer have a purpose.
For sensitive data, require an appropriate review before consent rather than relying on cleanup afterward. The exact controls should follow the platform’s documented capabilities and the organization’s requirements.
A review exercise that avoids live risky grants
Use a fictional permission request or a screenshot with no active authorization. Ask participants to identify the account, application, publisher, scope and task. Then ask what evidence is missing and where they would obtain it.
Do not score the exercise only on whether everyone refuses. A team that rejects every integration may also block useful work. The desired skill is recognizing the scope and finding a legitimate approval route.
Compare two versions of the same task: one with a narrowly explained permission request and one with unexplained broad access. Discuss what changed in the decision rather than teaching people to distrust a particular color or icon.
This is an editorial training exercise, not a validated measurement instrument. Its value is making the access decision visible enough to discuss.
What a good approval experience should communicate
The user should know why the app is present, who is responsible for it, what access it needs, how long the relationship is expected to last and how to remove it. If those answers require several unrelated help pages, the organization can simplify the process.
A useful internal approval message might say: “This approved calendar tool requests these specific permissions for this team workflow. Here is the owner and support route.” That is different from a generic instruction to click through whatever appears.
Avoid normalizing blanket approval during onboarding. If genuine training teaches people that every permission prompt is a nuisance to dismiss, later warnings will have less credibility.
Security controls should also provide a workable route when approval is denied. Otherwise, people may switch to personal accounts or unreviewed services to finish the task.
The decision after the button
The important moment is not simply before clicking Allow. It is understanding the state that exists afterward: another application may now act within the granted scope. That state can outlast the original email, meeting or document that persuaded you to approve it.
Treat consent as the creation of an access relationship, not as a decorative login step. Ask who receives it, what it permits and why it is needed. If the answers do not fit the task, pause.
Sources: Microsoft Entra consent-phishing guidance and Microsoft’s OAuth consent explanation. The review questions and organizational workflow are editorial analysis; exact permissions and revocation behavior are provider-specific.
Found a factual error or a source that has changed?
Send a correction →