Payroll changes deserve more than a familiar name in an inbox
A practical model for verifying direct-deposit changes, protecting employee portal access and handling urgent exceptions without improvised identity checks.
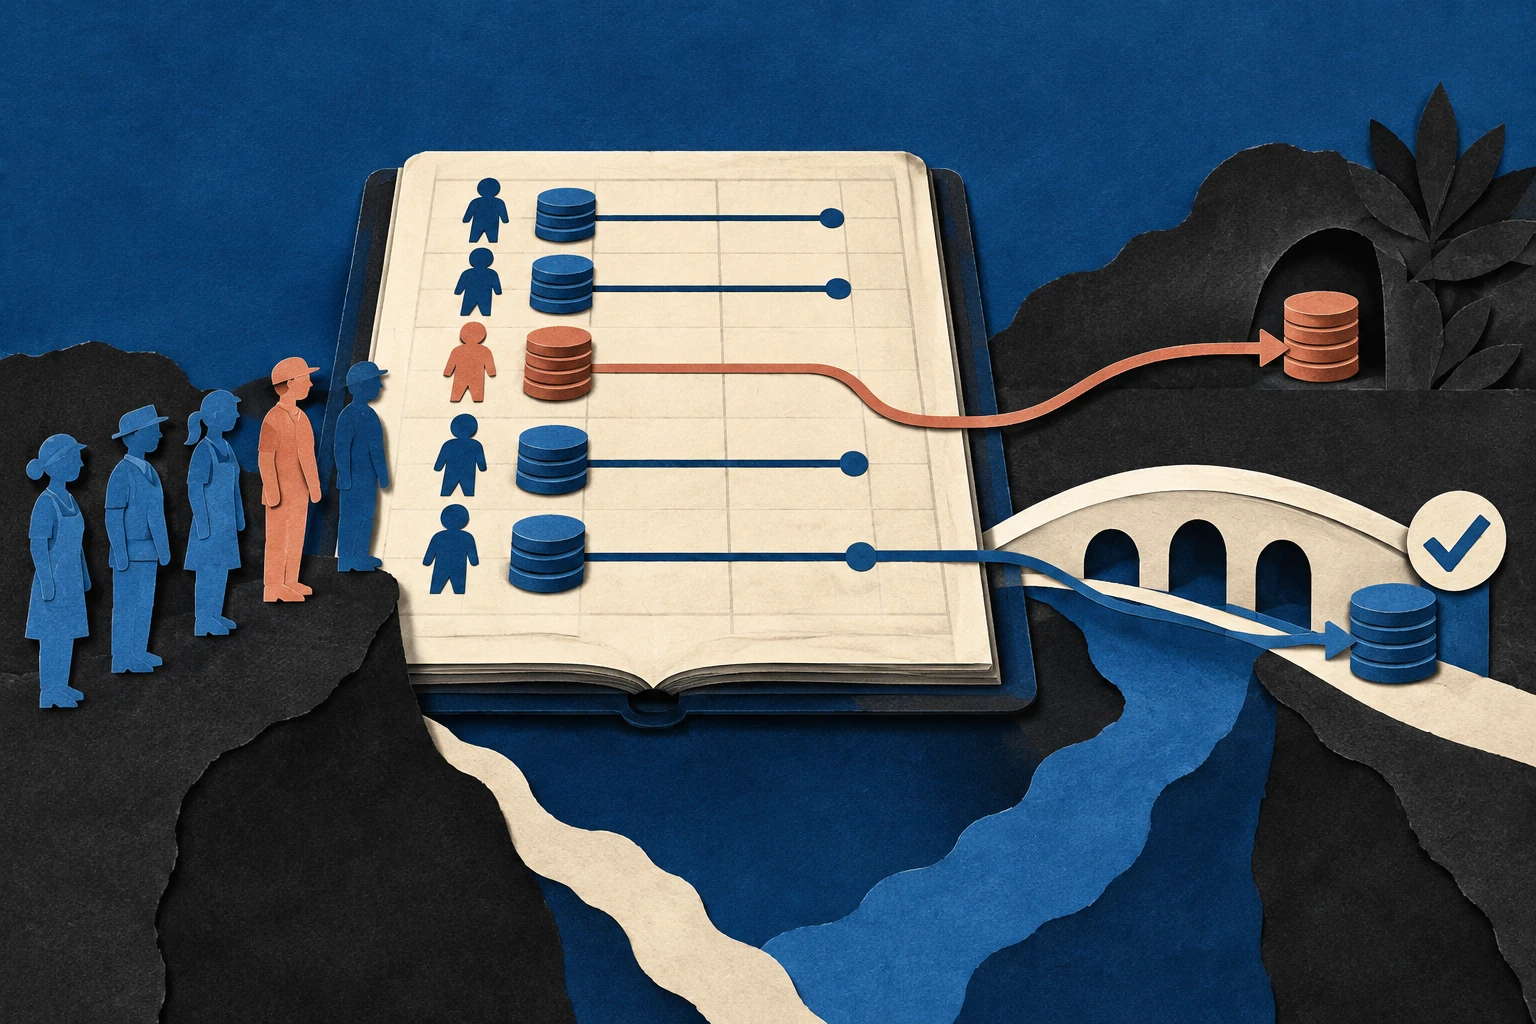
A payroll change often arrives wrapped in a completely ordinary story: a new bank, a closed account, a recent move or an employee who needs the next salary payment redirected. The request is sensitive, but the language may be mundane. That is exactly why it deserves a defined process.
For the employee, a misdirected salary can mean an immediate problem with rent, bills and family commitments. For payroll staff, the request arrives among deadlines and legitimate last-minute corrections. A procedure that works only when everyone has spare time will be weakest near the moment money moves.
The control is not “recognize the employee’s writing.” It is “verify this employee’s authority over this particular change.” That distinction remains important whether the request comes through email, a staff portal or a helpful-looking search result.
Two routes to the same payment problem
Someone asks payroll to change another person’s details.
Someone uses an employee’s account to make the change.
The next payment goes somewhere the employee did not authorize.
The first route tests the payroll team’s approval process. The second tests the employee’s sign-in and the controls around sensitive account changes. They can overlap, but investigating only one can miss the other.
A familiar sender name does not establish identity. A request submitted after a successful login is stronger evidence in some respects, but an authenticated session can still be misused. Payroll systems need to consider what action is being taken, not merely whether a session exists.
This is the same separation between identity and authority explored in our guide to helpdesk identity resets. A valid business need does not make every proposed recovery or change method acceptable.
What the FBI warnings say—and when
A 2025 FBI alert about employee self-service websites warns about impersonated employee portals used to steal information and funds. An older FBI San Diego payroll warning describes credential theft and unauthorized changes to direct-deposit details.
The older warning is historical context, not a new incident report. Together, the sources illustrate why both the route into a portal and the subsequent banking change matter. They do not establish that any particular employer or payroll provider is currently compromised.
The process recommendations below are our analysis. Exact controls depend on the payroll system, the organization’s responsibilities and applicable employment and privacy requirements.
Employees need a reliable route to the real portal
A saved, employer-provided portal address is more useful than asking workers to search for the payroll service whenever they need a payslip. Search results can contain advertisements and lookalike destinations alongside legitimate pages.
Give new starters a clearly documented access route through an established employer system. Explain how the organization announces genuine portal changes. If the address changes, a message that merely links to the replacement is a weak basis for teaching staff to distinguish it from an impersonation.
An employee who finds a different-looking login page should be able to confirm it without entering credentials first. The confirmation route must not be the support number displayed only on the questionable page.
The goal is not perfect domain-memory training. It is to reduce the number of times an employee must reconstruct a sensitive destination from a search result, a forwarded link or someone else’s assurance.
A payroll-change workflow with distinct checkpoints
| Checkpoint | Question it should answer | Weak substitute to avoid |
|---|---|---|
| Request origin | Did the employee initiate this request through an approved route? | A familiar display name |
| Employee verification | Is the requester authorized for this employee record? | Knowledge of a job title or manager |
| Change confirmation | Are the proposed details the employee’s intended change? | General approval to “update payroll” |
| Independent notification | Can the employee notice an unauthorized change promptly? | Notification only to newly changed contact details |
| Payment release | Has the approved change reached the correct pay cycle? | Assuming the portal and payroll batch always match |
Each checkpoint should have a responsible owner and a recorded outcome. A form containing all the fields is not proof that the checks happened.
Notification is especially useful when sent through a previously established route. However, an alert does not replace verification, and an employee may not see it immediately. The workflow should not treat silence as affirmative approval unless the organization’s carefully assessed process specifically supports that interpretation.
Why “I know the employee” is not enough
Payroll staff may know an employee’s manager, writing style and normal working hours. That familiarity helps service quality, but it does not make an email account immune to misuse.
The request may contain accurate personal information. Some information is public, some is shared within the workplace, and some may already be exposed. Asking for more biographical facts can create the appearance of verification without establishing control of an authorized account or channel.
Do not solve this by collecting unnecessary identity documents through ordinary email. A new collection of sensitive data creates its own storage, access and retention problems. Use the organization’s approved verification method and the minimum information it requires.
Our article on security questions and public facts explains why knowing details about a person is not equivalent to being entitled to act as that person.
Design the exception before the payroll deadline
A real employee can lose access to a phone, change a bank urgently or discover a mistake just before a cutoff. If the standard process offers no workable exception, staff will eventually invent one under pressure.
An exception should be authorized, documented and limited. It should identify what evidence substitutes for the unavailable normal check and who accepts the unresolved risk. “The employee sounded upset” is important service context, not a verification method.
Explain cutoff times and realistic alternatives before the last day of the pay cycle. People are more likely to follow a secure process when they understand its timing and can see what will happen next.
Avoid promising an immediate payment correction before the relevant bank and payroll team have confirmed the options. Speed matters, but a confident promise can create further distress when the payment mechanism cannot deliver it.
If the employee notices a change they did not make
Contact the employer’s established payroll and security routes promptly. State whether the change appears only in a portal, has entered a payroll run or has already resulted in a payment. That distinction helps the responsible team prioritize its response.
If credentials were entered on a suspicious page, report that separately. Use a trusted route and, where appropriate, a trusted device for account recovery. Follow the organization’s instructions rather than simply returning to the same questionable page to change the password.
Preserve the alert, the timing, the portal address encountered and the relevant payroll record. Do not publish salary details or account numbers while asking others to assess the situation.
A password change may be necessary, but it does not itself confirm that the bank destination has been corrected or that active sessions and connected access have been addressed. Those are separate checks.
If money has already gone to the wrong destination
The payroll team and relevant financial institution should assess available intervention or recovery options immediately. The employee should use known contact information, not a recovery service introduced through an unsolicited message.
Keep the payment reference and a clear timeline. Establish which party can speak to the sending bank and what information the employee needs to supply. Requiring a distressed employee to repeatedly retell the same story adds friction without adding verification.
Do not make blanket statements about reimbursement, liability or deadlines. Outcomes depend on the payment method, timing, jurisdiction, employment circumstances and the facts of the incident.
The employer should also consider the employee’s immediate practical needs through its established HR and payroll policies. Incident containment and humane communication are not competing priorities.
A useful test for managers and payroll teams
Run a tabletop exercise with invented employee and bank details. Include one straightforward request, one last-minute exception and one request arriving from an account that appears genuine but has not been independently checked.
Ask participants to show where they would find the employee’s established contact route. Check whether the person releasing payroll can see the verification record. Test what happens when the normal approver is absent.
Then examine the employee experience. Is the confirmation understandable? Does it identify the change without exposing unnecessary account details? Can the employee report a problem without using the same portal they suspect?
The exercise should reveal missing records and unclear ownership, not rank people by how suspicious they sound. A good process makes an unauthorized change difficult even when its wording is excellent.
The practical standard
The strongest outcome is not a payroll team that distrusts employees. It is a team that can help them quickly because the verification path is already understood. That protects both the salary payment and the relationship when a request arrives at the worst possible time.
Found a factual error or a source that has changed?
Send a correction →

